Find the destination
The visitor requests your custom domain. DNS resolves the Route 53 alias to CloudFront. The domain registrar’s nameservers must delegate to the correct public hosted zone.
Trace a request from the domain name through Route 53 and ACM-backed HTTPS to CloudFront and its authorized S3 origin. Follow each handoff and identify the configuration that makes it work.
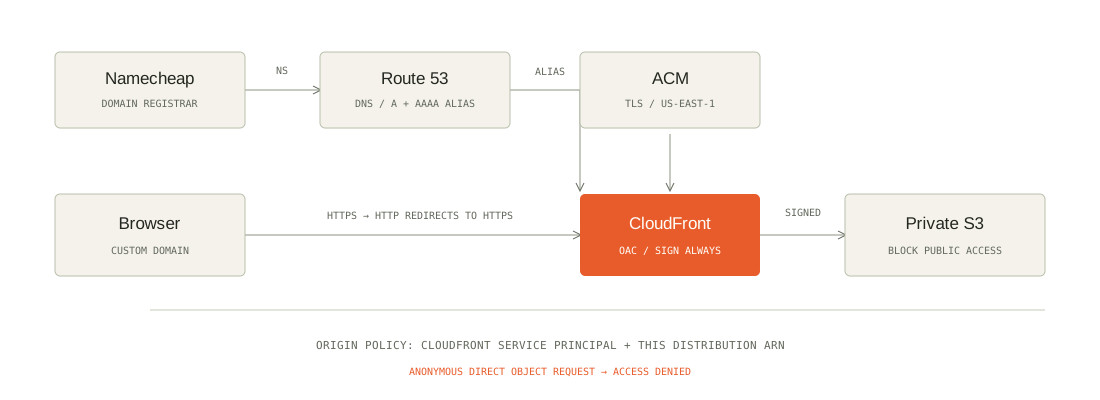
The visitor requests your custom domain. DNS resolves the Route 53 alias to CloudFront. The domain registrar’s nameservers must delegate to the correct public hosted zone.
The browser verifies that the TLS certificate is trusted and matches the hostname. HTTP requests are redirected to HTTPS by the distribution’s viewer protocol policy.
On an origin fetch, CloudFront signs its request. S3 evaluates the bucket policy, which permits GetObject for the CloudFront service principal only when the source distribution ARN matches.
CloudFront returns the object. The verification tools check status codes, content hashes, headers, certificate trust, DNS records, and anonymous S3 denial. A claim from an agent is not a substitute for these observations.